How a Leading Business Association Uses WSO2 to Unify Member Services
How a Leading Business Association Uses WSO2 to Unify Member Services
WSO2 Powers Tanzania’s #1 Fintech App: Mixx by Yas
WSO2 Changelog
- 10 Nov, 2026
New Asgardeo User Onboarding Wizard
Users signing into the Asgardeo Console are now guided through a new interactive onboarding wizard designed to get them to their first working login experience as quickly as possible.
WSO2 Accelerates Agentic Enterprise Adoption with New Agent Identity, Forward Deployed Engineers, and Expanded Delivery Partner Ecosystem
Austin, TX – May 21, 2026 – WSO2 today announced the expansion of its Agent Fabric platform, the introduction of a Forward Deployed Engineering model, and the scaling of its delivery partner ecosystem to accelerate the adoption of the agentic enterprise. Announced at the WSO2Con North America 2026, these initiatives strengthen WSO2’s position as the infrastructure layer for the emerging agentic enterprise, where AI agents operate autonomously across applications, APIs, workflows, identities, and data.
Introducing WSO2 Identity Server 7.3: Agentic AI, B2B CIAM, and Decentralized Identity
WSO2 Identity Server's goal is to make IAM simpler for developers without trading away the depth that production environments require. Version 7.3 advances that goal across three areas: securing AI agents that operate in the background, making B2B CIAM less complex, and bringing decentralized identity into the core product.
WSO2 Changelog
- 10 Nov, 2026
Mirror Registry Support for In-Dataplane Builds
Choreo now supports routing in-data-plane builds such as Argo Workflows running within a private data plane through customer-owned mirror registries including Nexus, Harbor, and JFrog Artifactory. Platform engineers can configure a single Kubernetes secret to redirect container image pulls and language package downloads (including npm, Maven, Gradle, NuGet, PyPI, Go, Composer, and RubyGems) away from public registries. This enables secure and reliable builds in restricted, private, or air-gapped Kubernetes environments.
WSO2 Changelog
- 10 Nov, 2026
M2M Usage Insights
Asgardeo now supports machine-to-machine (M2M) authentication insights, giving administrators visibility into M2M token issuance activity across their organization. Previously, the Insights view only surfaced user-driven activity such as logins and registrations, leaving M2M token usage as a blind spot for organizations relying on client credentials flows for service-to-service communication.
With this enhancement, administrators can now monitor M2M activity through a dedicated M2M view under Insights on the Asgardeo Console.
Documentation:
WSO2 Changelog
- 10 Nov, 2026
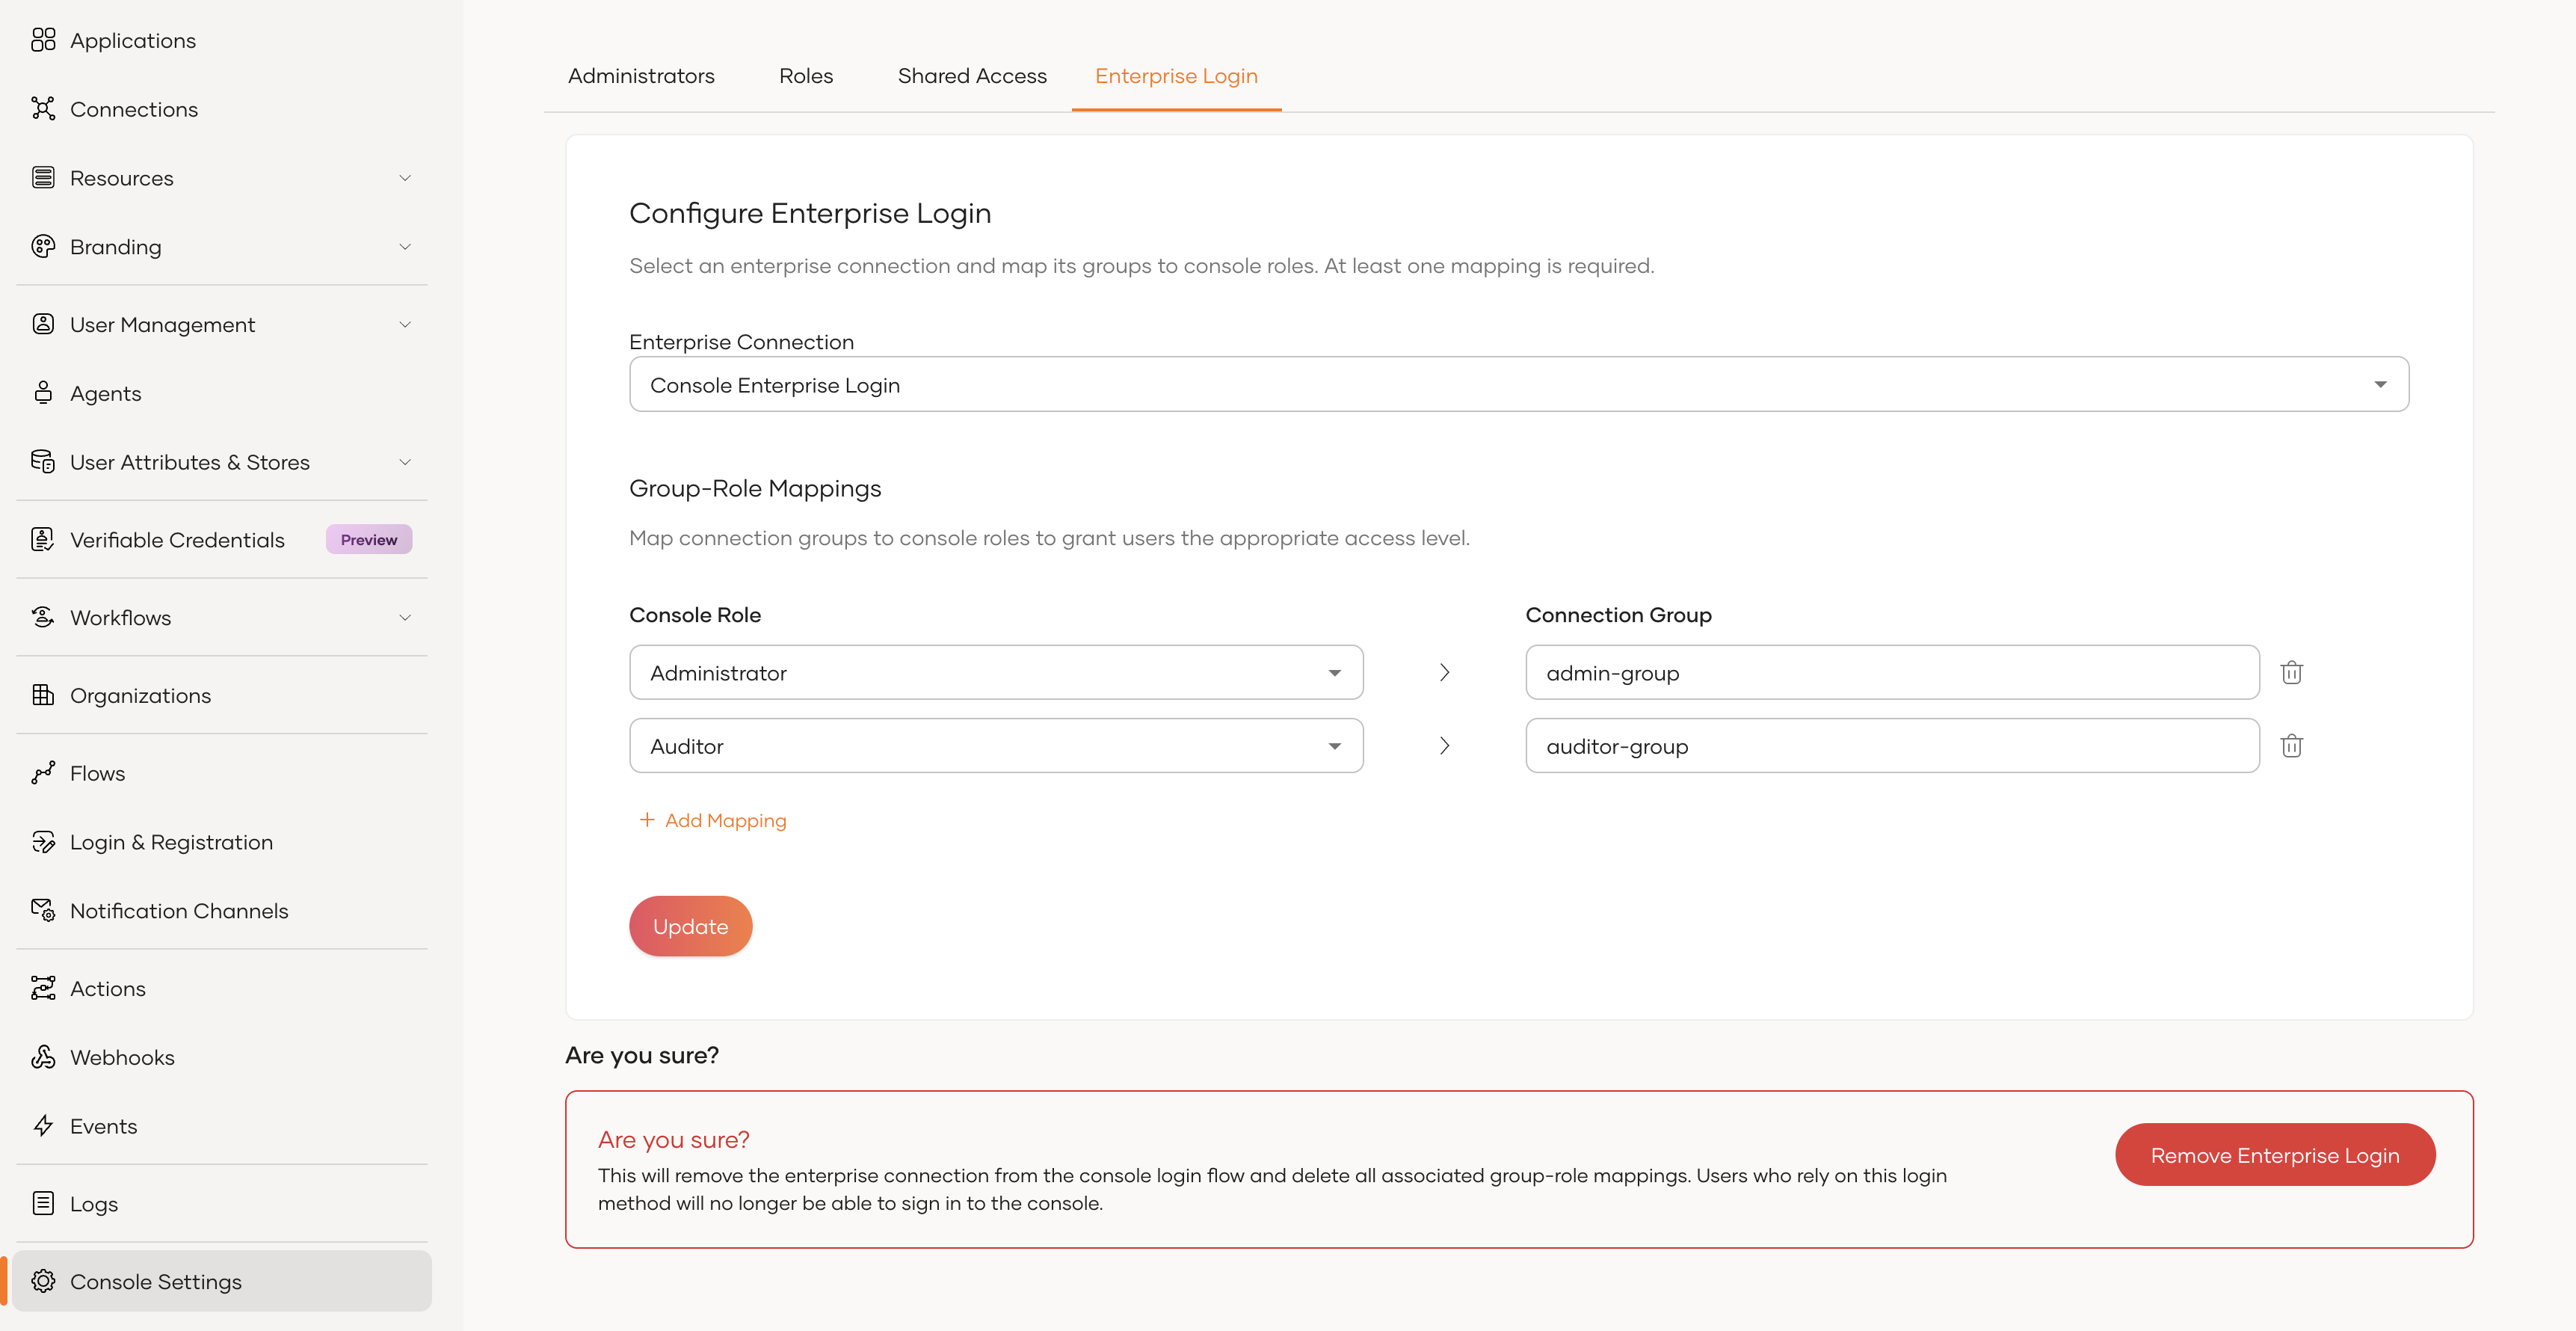
Asgardeo Enterprise Login
Asgardeo now supports enterprise login for the Console.
Enterprise login enables administrators to access the Asgardeo Console using credentials from an external identity provider (IdP). Instead of managing separate Asgardeo accounts, administrators can authenticate through their organization’s existing SAML or OIDC-based enterprise IdP, providing a more seamless and centralized sign-in experience.
WSO2 Changelog
- 10 Nov, 2026
Automatic Refresh for SAML IDP Certificates from Metadata URL
Asgardeo now supports using a SAML metadata endpoint as the certificate source for external SAML identity providers (Connections). With this enhancement, Asgardeo automatically retrieves and refreshes signing certificates from the configured metadata URL whenever a signature validation failure occurs, eliminating the need for manual certificate updates during IdP key rotations.
Key capabilities include:
WSO2 Changelog
- 10 Nov, 2026
Ability to Control OTP Resend/Retry from Adaptive Script (Outside the Authenticator)
Asgardeo now supports enhanced controls to govern OTP retry and resend attempts within a single authentication session, enabling administrators to mitigate brute-force attacks and optimize SMS/Email delivery costs while preserving a smooth user experience.
Key capabilities include: